Odido hackers claim to have hacked the FBI
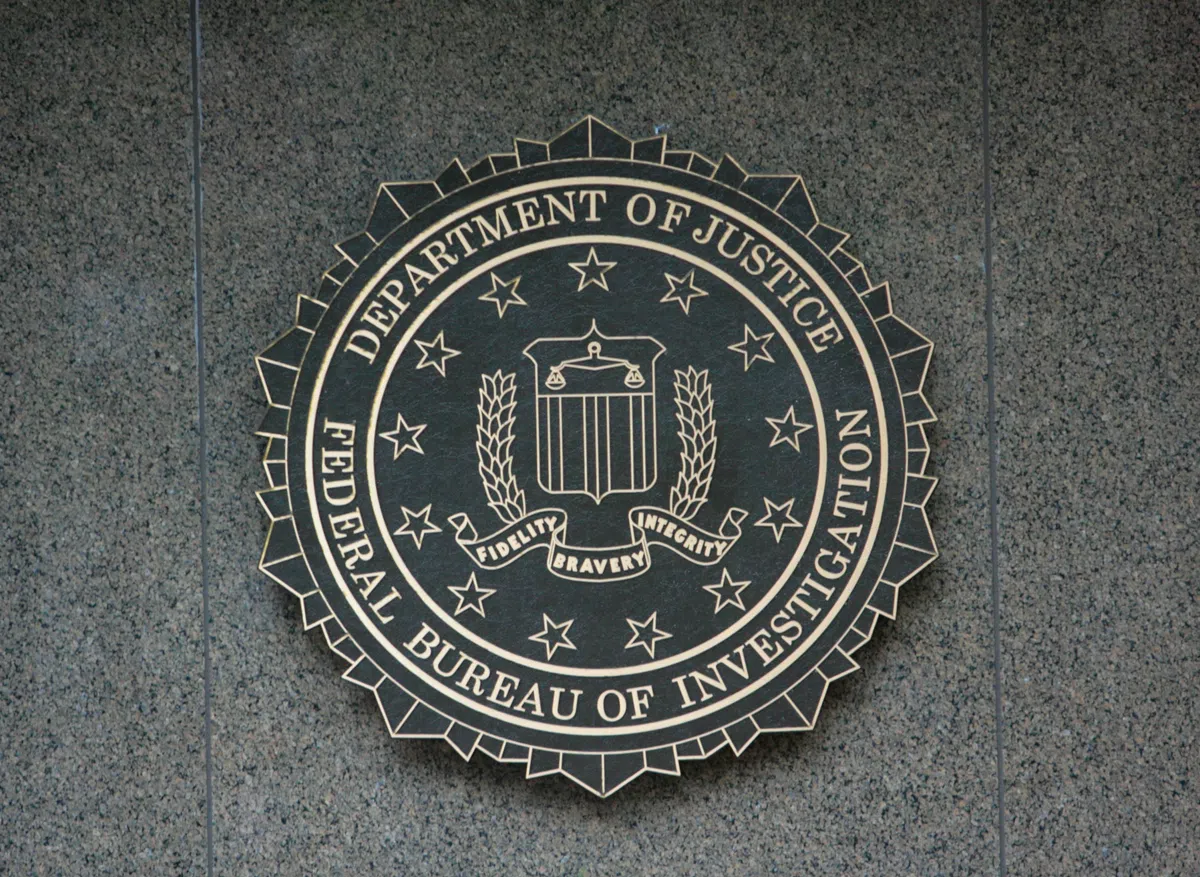
The recent claim by the hacking group ShinyHunters that they have gained access to confidential information from the FBI casts a shadow over cybersecurity within government institutions. The hackers are said to have stolen sensitive data of the entire FBI staff, including phone numbers, addresses, and other personal information. These revelations highlight the vulnerability of even the most secure organizations.
The implications of this breach are significant. If the hackers' claims are true, this could represent a serious violation of the privacy and security of FBI employees. Information about the personal lives of agents and their family members not only makes them susceptible to identity theft but could also jeopardize the safety of ongoing investigations and agents in the field. The question now arises how these hackers actually gained access and which security measures have failed.
The FBI has responded to these allegations by emphasizing that they are investigating the situation but has so far not released detailed information about the potential scope of the breach. The security of sensitive data is a top priority for many government institutions, but the constant threat of cyberattacks makes it a challenge to protect this information. It is crucial for organizations, both public and private, to continually evaluate and adjust their security measures to the ever-changing threats.
It is too early to say what the exact consequences of these data leaks will be and how they will affect the involved parties. The discussion around cybersecurity, the protection of personal data, and accountability of government entities will undoubtedly be further fueled by these incidents. In a world where digital attacks are becoming more frequent, it is of great importance that organizations, especially government institutions, remain proactive in their approach to cybersecurity.
Read the full article from Bright.
Gerelateerde artikelen

Insightful agenda for TechCrunch Founder Summit
The TechCrunch Founder Summit, taking place on November 4 in Boston, is aimed at supporting startup founders. The agenda is designed to provide them with valuable lessons, ensuring they don't have to...
Tech Festival
22 September 2026
Halo now in the hands of Activision after layoffs at Xbox
Xbox has recently undergone a large-scale reorganization, resulting in the loss of no less than 268 jobs. This restructuring affects various departments within the company but has a particular impact...
Tech Festival
22 September 2026
Snorkel AI raises valuation to $3.5 billion
Snorkel AI, a startup founded seven years ago, has recently achieved an impressive funding round of $350 million. This new capital strengthens the company's valuation to a staggering $3.5 billion. The...
Tech Festival
22 September 2026